While the full implementation of the Cyber Resilience Act (CRA) won’t take effect until December 2027, another critical milestone is already approaching much sooner. Starting from 11 September 2026, all manufacturers selling products with digital elements in countries of the European Union will be required to report actively exploited vulnerabilities in their digital products, as […]
Compass Security Blog
Offensive Defense
In this second part, we demonstrate how a Cyber Resilience Act (CRA) assessment is performed in practice. Using a low-cost IP camera as an example, we show how a product is classified, how threats are modelled, how hardware and firmware are analysed, and how compliance gaps against IEC 62443-4-2 can be identified. You may want […]
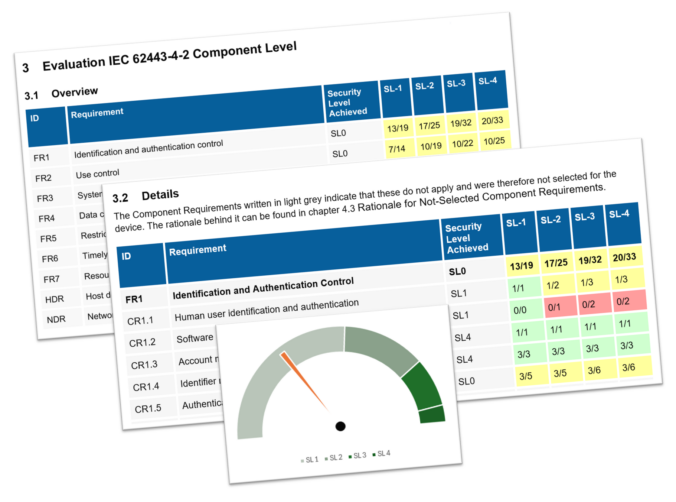
The Cyber Resilience Act (CRA) is a regulation introduced by the European Union to strengthen cybersecurity requirements for products with digital elements.In simple terms, the CRA sets mandatory cybersecurity rules for hardware and software sold in the EU. This includes everything from connected devices (IoT) to operating systems and even stand-alone software. Very important, this […]
© 2026 Compass Security Blog